
SonicWall TZ280
4.7Editor score
Up to 2.5 Gbps inspection
Eight Ethernet and two SFP ports
Broad next-generation security suite
Our expert guide compares the 10 best firewall appliances, covering ports, throughput, security features, ease of use, and hardware for homes or businesses.
Firewall appliances give homes, small offices, and branch networks a dedicated security boundary between trusted devices and external connections. A capable unit can centralize filtering, VPN access, threat protection, routing, and network visibility while reducing the burden on a general-purpose computer. The right appliance balances throughput, port flexibility, management options, hardware quality, and the ongoing security services required by the selected platform.
The ten products in this guide are compared using the supplied specifications, including processor capability, network interfaces, performance figures, form factor, included software, and service requirements. The list covers appliance-only and subscription-bundled models from Fortinet, SonicWall, Ubiquiti, Palo Alto Networks, Netgate, and Protectli. It also includes open-source-oriented hardware, so readers can distinguish between turnkey systems and appliances that require operating-system installation.
Each numbered review explains the strongest reasons to consider the appliance, along with limitations that deserve consideration before purchase. The top selections highlight particularly useful combinations of connectivity, performance, and usability, while the comparison table makes the core hardware differences easier to scan. Product prices and promotions change frequently, so confirm the current listing, service requirements, and software terms before ordering.
4.7Editor score

4.6Editor score

4.5Editor score
This side-by-side comparison highlights the main differences in port count, throughput, management model, and appliance type across all ten firewall appliances, from turnkey security systems to flexible mini-PC and open-source platforms.



The Protectli Vault FW4B earns a rating of 4.6 and stands out as a compact mini-PC designed specifically for network-security workloads. Its Intel Celeron J3160 processor provides four cores, clock speeds up to 2.2 GHz, and hardware AES-NI support, while four Intel Gigabit Ethernet ports create a practical foundation for a dedicated firewall. The appliance is not tied to one proprietary interface, which gives it unusual flexibility for a home lab, small office, or technically capable enthusiast.
We may earn a commission when you buy through this link, at no additional cost to you.
Its most important strength is the ability to run popular open-source firewall environments. The supplied information confirms hardware testing with pfSense, Untangle, and OPNsense, as well as other open-source solutions. That makes the FW4B a blank platform rather than a finished security system: an administrator can install the operating system that best matches the required features, interface, and support preferences. The included 8GB of DDR3L memory and 120GB mSATA SSD provide room for the operating system, logs, packages, and configuration data.
Physical connectivity is well suited to a small secure edge. The four Gigabit Ethernet ports can support WAN and LAN arrangements, while two USB 3.0 ports and two HDMI outputs make the unit practical to configure locally. A serial RJ-45 COM port is also available. The fanless enclosure is designed for silent operation, and the 64-bit processor includes AES-NI, a valuable feature for networks that use encrypted services or VPN workloads. A coreboot BIOS is optional and must be installed by the user.
The trade-off is that this is not an appliance in the traditional turnkey sense. No operating system is preinstalled, and buyers must create or obtain the installation media, configure boot order, install software, and understand the selected firewall interface. For many technically experienced users, that freedom is an advantage. For someone who wants a preconfigured appliance with a vendor console, the Fortinet, SonicWall, Netgate, and Ubiquiti alternatives may be easier to deploy.
The FW4B is best for users who value control, compatible software ecosystems, and quiet hardware that can remain dedicated to firewall duties. It is also a strong match for homelab environments and small networks where a general-purpose computer would be less tidy. Choose it when you want a flexible security platform and are comfortable with setup, and favor a turnkey system when immediate guided operation matters more.
Because the operating system is not preinstalled, the FW4B can be tailored to pfSense, Untangle, OPNsense, or another compatible solution. This makes the hardware easier to align with a preferred interface, feature set, and administrative workflow.
The fanless enclosure minimizes noise, while AES-NI and four Gigabit Ethernet ports support the demands of a compact home or small-office firewall. Eight gigabytes of RAM also provides more headroom than many similarly compact appliances.
We may earn a commission when you buy through this link, at no additional cost to you.
The FortiGate-60F combines a 4.4 rating with unusually dense connectivity for a compact business firewall. Its ten Gigabit Ethernet RJ45 ports include two WAN connections, one DMZ port, and seven internal ports, allowing administrators to build a more segmented network without immediately adding another device. Fortinet’s security processor and dedicated architecture support up to 1.4 Gbps IPS throughput and 700 Mbps threat-protection throughput.
We may earn a commission when you buy through this link, at no additional cost to you.
FortiGate devices are intended for organizations that want integrated networking, threat prevention, SSL inspection, and application-aware policy in one platform. The FortiGate-60F adds robust SD-WAN functionality, encrypted-traffic inspection, a management console, network automation, and visibility tools. Zero Touch Integration with Fortinet’s Security Fabric is intended to simplify deployment, particularly for administrators working with supported infrastructure and cloud environments.
A key buying consideration is that this listing is appliance only and does not include a subscription. The hardware is the foundation, but security services, firmware updates, and support may require a separate purchase. Buyers should determine exactly what the appliance can do without a service subscription and which FortiGuard features are necessary for their environment. This model and the included-service bundle in this guide offer similar hardware, but different acquisition structures.
The trade-off is complexity relative to a simple home router. Ten ports, dedicated threat processing, SSL inspection, SD-WAN, and ecosystem integration provide substantial capability, but they also create a broader configuration surface. Administrators should plan a security policy, segment internal and DMZ systems, and account for subscription requirements before treating the unit as a complete security solution.
The FortiGate-60F is a strong recommendation for small and medium-sized businesses, branch offices, and technically capable home networks that need more ports and sophisticated security than a basic consumer gateway. It is particularly compelling when Fortinet management, SD-WAN, and the broader Security Fabric ecosystem are already part of the network strategy.
Dedicated WAN, DMZ, and internal interfaces support a clearer network design. This is valuable for businesses isolating public services or operating several wired segments without relying on a single shared LAN port.
The stated IPS and threat-protection throughput figures show the value of dedicated security hardware. SSL inspection and SD-WAN support further extend the appliance beyond basic packet filtering.
We may earn a commission when you buy through this link, at no additional cost to you.
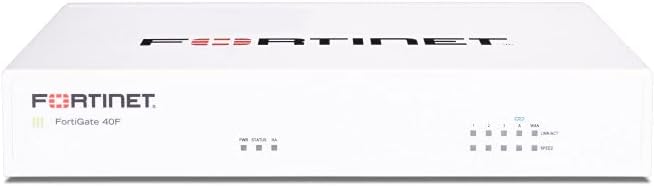
The FortiGate-40F is designed for small and mid-sized businesses and enterprise branch offices, and its 4.2 rating reflects a practical balance of compactness and protection. It has five Gigabit Ethernet RJ45 ports divided between one WAN interface and four internal ports. That is enough for a compact business network, a protected branch, or a home lab requiring more control than a basic consumer router provides.
We may earn a commission when you buy through this link, at no additional cost to you.
Inside, Fortinet’s purpose-built security processor supports up to 1 Gbps IPS throughput and 600 Mbps threat-protection throughput. The appliance also uses AI-powered FortiGuard Labs intelligence to identify and mitigate known and unknown threats, with a focus on encrypted traffic. Its management console combines automation and visibility, while Zero Touch Integration with the Security Fabric can streamline initial deployment.
The fanless desktop enclosure is convenient for offices where appliance noise would be distracting. Its smaller port count makes it less suitable for highly segmented environments or for connecting numerous wired network segments, but that limitation also keeps the design straightforward. The five-port layout is usually ample for a small business with a modem or upstream connection, a firewall gateway, and several internal devices.
As with the FortiGate-60F appliance-only listing, security services, updates, and support are not bundled. Users need to understand Fortinet’s subscription structure before deployment. The broader feature set can also be more involved than required for a basic home network, so buyers should avoid paying for unnecessary capabilities when a simpler platform would meet the requirement.
Choose the FortiGate-40F for a quiet, compact business gateway with meaningful inspection capability and Fortinet’s management ecosystem. It is a better fit than a higher-port model when a single WAN and several internal connections are the practical requirement, and a better fit than an appliance-only listing when a smaller, easier-to-place footprint matters.
The fanless desktop form factor reduces noise and needs little space. It can sit near network equipment without behaving like a noisy general-purpose desktop.
One WAN and four internal ports cover a conventional small-office topology. The result is simpler than a ten-port model while retaining dedicated inspection and threat-protection hardware.
We may earn a commission when you buy through this link, at no additional cost to you.
The Ubiquiti Unifi Security Appliance offers a straightforward way to add firewall, routing, and VPN functions to a UniFi-managed network. It has a 4.5 rating, a clean white enclosure, and a compact form factor that can sit on a desk or mount on a wall. Its strongest appeal is integration: users who already depend on Ubiquiti devices and the UniFi Controller gain a consistent management experience.
We may earn a commission when you buy through this link, at no additional cost to you.
Despite its simple exterior, the USG includes meaningful network features. It supports VLANs, which help separate guest, employee, IoT, and other device groups, and provides QoS capabilities aimed at enterprise VoIP. A built-in VPN server supports secure remote communications, while 10/100/1000Base-T connectivity and Gigabit Ethernet ports suit modern wired networks.
Three ports—one identified as the management port and the others as Gigabit Ethernet network interfaces—make the device appropriate for compact networks. It can serve a modest home, a small office, or a UniFi access-point environment where centralized control is more important than a large number of wired interfaces. The appliance can be deployed as a desktop unit or wall-mounted, which helps conserve shelf space.
The limitation is ecosystem focus and limited physical scalability. Users without UniFi infrastructure may find the appliance less compelling than a more independent firewall platform, and three ports leave little room for expansion without another switch or network device. The device also concentrates on practical gateway functions rather than the extensive high-end security processing advertised by some dedicated business appliances.
This is the best budget-oriented choice for a buyer who wants capable firewall features in a compact, well-integrated unit. It is particularly attractive to small organizations and advanced home users that standardize on UniFi equipment and prioritize VLAN organization, QoS, and straightforward centralized management over extensive physical interfaces.
Controller integration reduces the number of separate administration environments. Users can manage the firewall within the same ecosystem used for compatible access points and network switching.
VLAN support and enterprise VoIP QoS provide useful tools for separating traffic and prioritizing voice communications. These features make the USG more versatile than a basic wired router.
We may earn a commission when you buy through this link, at no additional cost to you.
The SonicWall TZ280 has a 4.7 rating and the highest stated firewall-inspection rate in the group: up to 2.5 Gbps. It also delivers 1 Gbps threat-prevention throughput and 1.2 Gbps IPSec VPN throughput, making it well suited to small businesses and branch sites where performance and security depth are both priorities. The desktop appliance uses SonicWall’s Reassembly-Free Deep Packet Inspection engine.
We may earn a commission when you buy through this link, at no additional cost to you.
Connectivity is unusually flexible for the size. Eight one-gigabit Ethernet ports and two one-gigabit SFP interfaces provide ten physical connections, with SFP options useful for longer network links or compatible fiber modules. Zero-touch deployment and on-box or cloud Network Security Manager support can help administrators bring the unit into service with less repetitive setup work.
SonicOS 8 covers intrusion prevention, gateway anti-malware, application control, TLS and SSL decryption, Capture ATP multi-engine sandboxing, and reputation-based content and DNS filtering. The appliance also supports secure SD-WAN, IPSec and SSL VPN, and Zero-Trust Network Access through Cloud Secure Edge. Together, these functions create a broad platform for distributed sites and remote workers.
The important caveat is that the listing is hardware only. Security services, firmware updates, and support are not included and must be purchased separately to activate protection. This makes the total ownership picture different from a turnkey unit with preloaded software, even though the hardware is capable. Buyers should confirm which subscription level matches the advanced features they intend to operate.
The TZ280 is a compelling premium selection for organizations seeking serious inspection performance, modern application controls, VPN options, and centralized management in a compact form factor. It is a better fit than simpler units when traffic volume, remote access, branch connectivity, and zero-trust requirements justify a full next-generation security platform.
The 2.5 Gbps firewall-inspection figure provides substantial capacity for modern networks. Separate threat-prevention and IPSec VPN figures help buyers judge more demanding workloads.
Application control, anti-malware, SSL decryption, sandboxing, and reputation filtering create a comprehensive security layer. SD-WAN and Zero-Trust support extend those capabilities to distributed environments.
We may earn a commission when you buy through this link, at no additional cost to you.
The Netgate 1100 pfSense+ combines a dedicated security gateway with preloaded pfSense+ software, making it one of the more approachable open-platform products in this guide. It has a 4.1 rating, a dual-core ARM Cortex-A53 processor running at 1.2 GHz, and three switched Gigabit Ethernet ports that can be assigned as WAN, LAN, or optional interfaces. It is aimed at users who want the flexibility of pfSense without installing the operating system themselves.
We may earn a commission when you buy through this link, at no additional cost to you.
The supplied specifications state firewall throughput in excess of 650 Mbps and near-gigabit routing for common home iPerf3 traffic. That makes the appliance suitable for many residential and small-office connections, although its firewall performance does not reach the 1 Gbps or greater inspection figures advertised by several dedicated business units. The distinction matters when encrypted traffic, large file transfers, or high-volume inspection are central to the use case.
Netgate includes pfSense+ software updates for the product’s lifetime, Netgate TAC Lite technical support, and a one-year hardware warranty. Setup assistance is also available from the Technical Assistance Center around the clock. The appliance can be placed on a desk, wall, or rack and uses a compact, low-power, silent design, making it convenient for homes and small offices.
Three ports are the main constraint. A typical deployment uses one for the upstream connection and two for internal networks, but adding more segments or wired devices may require an external switch. The supplied listing also notes that delivery requires an adult signature, an operational detail worth recognizing before ordering.
Choose the Netgate 1100 when you want a ready-to-configure pfSense+ system with support and lifetime software updates. It is an excellent middle ground between a plug-in consumer router and a bare-metal mini-PC, particularly for technically engaged users who value the pfSense interface without wanting to handle operating-system installation.
Preloaded pfSense+ software removes the installation step associated with many mini-PC firewalls. Included technical support provides a path for resolving configuration questions.
The Cortex-A53 platform offers useful routing and firewall capacity in a silent, low-power enclosure. It is best matched to residential and small-office traffic rather than heavily inspected enterprise links.
We may earn a commission when you buy through this link, at no additional cost to you.
The FortiGate-100E carries a 4.7 rating and is positioned as a network security appliance for organizations that need more than basic packet filtering. The supplied information emphasizes protection against known exploits, malware, and malicious websites, detection of unknown attacks, and identification of thousands of applications. These capabilities point toward centralized, application-aware policy rather than a simple home internet gateway.
We may earn a commission when you buy through this link, at no additional cost to you.
Application identification is particularly valuable in a business environment because it helps administrators understand and control how users interact with network services. Unknown-attack detection adds another layer beyond maintaining a list of known signatures, while blocking malicious websites and malware helps reduce exposure to common online threats. Together, these features support a more structured security strategy for managed networks.
The listing is part of the FortiGate family, which also appears elsewhere in the guide with more detailed connectivity and throughput information. Because the supplied data for the 100E focuses on its protection capabilities rather than port count, processing figures, form factor, or included services, buyers should not assume it has the same interface layout as the FortiGate-40F or FortiGate-60F. Exact specifications should be confirmed with the manufacturer or listing documentation.
Subscription and lifecycle considerations are also important. Fortinet appliances commonly use security subscriptions and service bundles for threat intelligence, updates, firmware, and support. Since the supplied product information does not state which of those are included, this model should be purchased only after confirming the current terms for the exact configuration and account requirements.
The FortiGate-100E is best suited to administrators who value comprehensive Fortinet threat protection and application control. Its high rating and enterprise-oriented security description make it worth a closer look, while the limited hardware details mean it is less straightforward for casual buyers than the fully specified FortiGate-40F and FortiGate-60F.
Detection of unknown attacks broadens the appliance’s value beyond blocking a fixed catalog of known threats. This capability is relevant when organizations want layered defenses against evolving traffic.
Identifying thousands of applications supports more precise policies. Administrators can apply controls based on the type of traffic rather than treating every connection as an undifferentiated flow.
We may earn a commission when you buy through this link, at no additional cost to you.
The Palo Alto PA-220 is an eight-port next-generation firewall appliance from a well-known enterprise security vendor, but its 3.0 rating is the lowest in this comparison. The supplied listing describes it as new and identifies the model as PAN-PA-220, giving buyers a clear product identity without offering a detailed breakdown of throughput, processor capabilities, dimensions, management options, or included subscriptions.
We may earn a commission when you buy through this link, at no additional cost to you.
An eight-port design is a meaningful advantage for network segmentation. It can provide a combination of WAN, internal, DMZ, or service interfaces, although the exact assignment and supported configurations depend on the operating mode and license level. Next-generation firewalls generally focus on application-aware inspection and policy control, making this model relevant to administrators seeking more detailed traffic analysis than a basic router provides.
The limited listing information is a major factor in the rating and in how cautiously this recommendation should be interpreted. Performance, supported protocols, throughput, subscription requirements, and compatibility with current management systems should be verified before purchase. Palo Alto Networks appliances also involve licensing considerations that can affect which security services and support are available, so the buyer should examine the exact package rather than assume standard protection is included.
The PA-220 may appeal to buyers who specifically want the Palo Alto platform and have an eight-port requirement. However, buyers who want abundant published specifications and a clearer understanding of what is included may find the FortiGate models, SonicWall TZ280, Netgate 1100, or Protectli appliances easier to evaluate from the available product data.
This is a conditional recommendation rather than a universal one. Consider the PA-220 when its eight-port design, next-generation firewall category, and Palo Alto ecosystem fit an existing network plan, but verify current licensing and technical details. It is less suitable for a buyer who needs a simple, immediately understandable purchase without additional research.
The port count provides more physical options than the three-port units in the guide. It can suit a small branch or service-rich internal network when configured for the required roles.
Next-generation firewall features often depend on licensing and management integration. Buyers should confirm that the specific PA-220 package supports the policies and services they actually intend to operate.
We may earn a commission when you buy through this link, at no additional cost to you.
The Protectli Vault FW4C distinguishes itself with four 2.5 Gigabit Ethernet ports, a meaningful step up from conventional Gigabit-only compact firewalls. It has a 4.5 rating and uses an Intel J3710 Pentium quad-core processor with four threads, a base clock of 1.6 GHz, and burst capability up to 2.6 GHz. Intel AES-NI support helps accelerate cryptographic operations, while the fanless enclosure keeps the unit compact and silent.
We may earn a commission when you buy through this link, at no additional cost to you.
Its central strength is multi-gigabit connectivity. The four Intel 2.5GbE interfaces create a high-speed platform for modern networks, NAS equipment, fast local storage, and multi-gigabit broadband or switches. That makes the FW4C especially interesting for advanced home labs and small offices that want to avoid limiting internal traffic to one gigabit per second.
As with the FW4B, no operating system is preinstalled. The hardware has been tested with pfSense, Untangle, OPNsense, and other popular open-source solutions, allowing the software to be chosen according to the buyer’s preferred interface and feature set. Two USB 3.0 ports, two HDMI outputs, and an RJ-45 COM port are also provided for setup and peripheral needs.
The specifications include 4GB of DDR3 RAM and a 32GB SSD. That is a more modest configuration than the FW4B’s 8GB and 120GB, and the difference may matter when running memory-heavy packages, retaining extensive logs, or installing additional services. The FW4C should therefore be judged as a faster-network, leaner-storage model rather than a universal upgrade over every FW4B configuration.
The FW4C is best for users with genuine multi-gigabit requirements who value open-source flexibility and quiet dedicated hardware. It may be less suitable for general home users who will never exceed Gigabit speeds or for administrators who need abundant storage without opening the unit to upgrade components.
Four 2.5GbE interfaces avoid the bottleneck of a single Gigabit uplink. The platform is well suited to fast switches, network storage, and newer local connectivity standards.
The same broad operating-system compatibility as the FW4B makes the platform adaptable. Its smaller RAM and storage configuration keeps the appliance focused, but leaves less expansion headroom.
We may earn a commission when you buy through this link, at no additional cost to you.
This FortiGate-60F bundle combines the appliance with one year of FortiGuard Unified Threat Protection and one year of FortiCare Premium support. Its 4.2 rating reflects a product designed for medium-sized businesses that want robust security without the infrastructure of a larger enterprise. Unlike an appliance-only purchase, the package begins with both the hardware and a defined period of threat-protection services and support.
We may earn a commission when you buy through this link, at no additional cost to you.
Unified Threat Protection provides web filtering and anti-botnet technologies designed to address online threats. These are broad defensive controls for organizations that want managed threat intelligence and filtering rather than manually maintaining every rule. FortiCare Premium adds a support component, which can be valuable during deployment, troubleshooting, and ongoing administration.
The underlying FortiGate-60F platform is the same general family as the separate appliance-only product listed earlier in this guide. It is aimed at organizations that need more substantial security than a basic internet router but do not need enterprise-scale infrastructure. Buyers should nevertheless verify the current licensing terms and confirm that the included protection meets their required applications and support expectations.
The central trade-off is renewal economics and potential overpayment. Buyers comparing this package with the appliance-only alternative should determine whether they will use the included web filtering, anti-botnet protection, and support during the covered period. If they will, the bundle can reduce initial uncertainty; if not, an appliance-only purchase may be more appropriate. Subscription renewals also need to be included in long-term planning.
The bundle is best for a medium-sized organization seeking a business firewall with a defined first year of managed security and premium support. It is particularly helpful for administrators who want a complete starting package and can justify the subscription after the initial term.
Bundling one year of FortiGuard Unified Threat Protection and FortiCare Premium gives the buyer immediate access to managed filtering and support resources. It reduces the need to assemble the initial service package separately.
The initial service period does not remove the need to budget for continuing protection. Compare the bundle with appliance-only hardware based on the security services the organization will actively use.
We may earn a commission when you buy through this link, at no additional cost to you.
Choosing a firewall appliance means matching security capabilities, physical connectivity, and operating requirements to the network. The most important decisions are how the device will be managed, how much traffic it must inspect, which ports are needed, and whether ongoing security subscriptions are acceptable.
A turnkey appliance includes an operating system or vendor-managed interface and is generally easier to deploy. The Netgate 1100 arrives with pfSense+ preloaded, while Fortinet, SonicWall, Ubiquiti, and Palo Alto products are designed around their respective management environments. By contrast, the Protectli FW4B and FW4C ship without an operating system, giving administrators freedom to select pfSense, Untangle, OPNsense, or another compatible solution. That freedom is attractive for technical users but creates responsibility for installation, updates, and troubleshooting.
Firewall hardware is only one part of a security solution. The SonicWall TZ280 listing explicitly excludes services, firmware updates, and support, while the FortiGate-60F bundle includes one year of FortiGuard Unified Threat Protection and FortiCare Premium. Fortinet appliance-only listings also require separate service consideration. Before ordering, identify which threat intelligence, filtering, updates, support, and advanced inspection features you need and whether they are included.
Count the required WAN, LAN, DMZ, and management connections rather than choosing by total ports alone. The FortiGate-60F provides ten RJ45 ports, while the FortiGate-40F supplies five and the Netgate 1100 and Ubiquiti USG provide three. The SonicWall TZ280 combines eight copper ports with two SFP interfaces, and the Protectli units offer four Gigabit or 2.5GbE ports. SFP and multi-gigabit interfaces can provide more flexibility when a network requires fiber, longer links, or faster local traffic.
Firewall throughput figures generally describe different processing tasks, so they should not be treated as interchangeable. The SonicWall TZ280 is rated for up to 2.5 Gbps firewall inspection, the FortiGate-60F for 1.4 Gbps IPS throughput, and the FortiGate-40F for 1 Gbps IPS throughput. The Netgate 1100 offers more than 650 Mbps of firewall throughput. Applications such as SSL inspection, threat prevention, VPN, and large file transfers can reduce practical speed, so select a model with headroom above expected traffic.
A feature-rich firewall is only useful if the administrator can operate it confidently. Ubiquiti USG is attractive for users already managing UniFi equipment, Netgate users receive a familiar preloaded pfSense+ environment, and Fortinet environments benefit from the management console, automation, and Security Fabric integration described in the product information. Open-source mini-PCs provide deep control but require more hands-on setup. Match the interface and subscription model to the skills available for ongoing maintenance.
A firewall is often purchased because a network must support remote users, branch connectivity, or separated trust zones. The Ubiquiti USG includes a VPN server, the Netgate 1100 supports VPN functions, and the SonicWall TZ280 provides IPSec and SSL VPN along with SD-WAN and Zero-Trust Network Access. VLAN support on the Ubiquiti unit can also improve local segmentation. Identify whether the requirement is basic remote access, site-to-site tunnels, application-aware inspection, or a broader zero-trust architecture.
A firewall may remain powered continuously, so physical design affects everyday use. The FortiGate-40F and both Protectli Vault models use compact fanless designs intended for quiet operation. The Netgate 1100 also emphasizes a compact, silent enclosure and can be placed on a desk, wall, or rack. Ubiquiti’s USG is wall-mountable, and the SonicWall TZ280 uses a desktop form factor. Consider available space, cable reach, ventilation, and whether the device will be visible in a living area or office.
Compact appliances can differ significantly in memory and storage even when they share a form factor. The Protectli FW4B includes 8GB of RAM and a 120GB mSATA SSD, while the FW4C includes 4GB and 32GB. Those differences may influence package selection, log retention, and optional services. Buyers of open-platform hardware should investigate supported upgrades before installation. For proprietary appliances, confirm expansion limits, expected service life, and whether the current product generation is appropriate for the deployment.
Begin by documenting the existing network, including the upstream connection, router, modem, public services, VLANs, VPN users, and connected devices. Install the appliance in a central location with unobstructed access to its ports and power, then connect the upstream link before moving internal traffic to it. Photograph the original cabling and record each interface’s role. For open-platform units, use trusted installation media, select the intended firmware or operating system, and apply updates before exposing the device to production traffic.
Build a security policy in stages rather than enabling every inspection feature at once. Create rules that permit necessary traffic, restrict unnecessary inbound connections, and define appropriate access between trusted, guest, IoT, and externally exposed systems. Where supported, enable logging and reporting, configure DNS filtering and malware controls, and test VPN access with a representative client. Changes should be saved and backed up, with an emergency recovery plan established before a remote-access rule or critical routing change is applied.
Ongoing care includes monitoring processor utilization, memory pressure, session capacity, and logged security events. Update firmware and security subscriptions through the vendor’s approved process, and keep the management interface restricted to authorized administrators. Preserve airflow around the chassis, clean dust from vents gently, and use surge protection or a properly grounded power source. Periodically test restoration from a configuration backup and review firewall rules, user access, exposed services, and subscription status to prevent policy drift.
A home router usually combines routing, Wi-Fi, and basic packet filtering, while a dedicated firewall appliance places more emphasis on centralized policy, VPN support, threat inspection, segmentation, and detailed reporting. Some appliances also provide routing functions and can replace a separate router. The right choice depends on the network’s complexity, required protection, management expertise, and whether Wi-Fi is provided by separate access points.
Many firewall appliances can perform routing, so a separate router may not be required. For example, the Netgate 1100 explicitly includes firewall, router, and VPN functions, while Protectli units can run routing-capable firewall software. A separate router may still be useful for a simple upstream connection, advanced Wi-Fi features, or a specific network design. Confirm the operating mode and required interfaces before removing existing equipment.
They require more initial setup because no operating system is preinstalled, but they can offer broad control and product choice. The Protectli FW4B and FW4C have been tested with pfSense, Untangle, OPNsense, and other popular open-source solutions. Ongoing work includes updates, backups, monitoring, and troubleshooting, so users should be comfortable with basic administration or have technical support available.
Inspection throughput estimates how quickly an appliance can process traffic while applying specified security functions. It is not identical to plain routing speed, and features such as SSL inspection, intrusion prevention, threat filtering, VPN, and application control can affect real-world performance. Compare a product’s figures only when the tested functions and traffic conditions are similar.
No. An appliance-only purchase generally provides the hardware, while threat intelligence, security subscriptions, firmware updates, or support may be separate. The SonicWall TZ280 listing explicitly notes that services and updates are not included, and appliance-only FortiGate purchases should be evaluated on the same basis. The FortiGate-60F bundle in this guide includes one year of FortiGuard UTP and FortiCare Premium for comparison.
Count the upstream WAN, internal LANs, management connection, DMZ, and any additional service interfaces. Three ports can be enough for a simple network, five may suit a small office, and eight or ten provide more room for segmentation. Multi-gigabit or SFP ports can be valuable for fast switches, fiber links, or local network storage, but the total count should follow an actual network design rather than a desire for extra connectors.
A firewall appliance is a central layer, not a complete security solution. It should be combined with endpoint protection, strong authentication, secure configuration, patching, monitoring, backups, and user awareness. A business should also assess which advanced protections are actually required and whether the relevant services and support are licensed for the selected appliance.
A 2.5GbE firewall is most useful when the internet connection, local switch, network storage, and internal devices can all sustain more than one gigabit. The Protectli FW4C provides four 2.5GbE ports and can prevent a multi-gigabit local network from being limited by an older gateway. If most traffic is ordinary Gigabit Ethernet, a Gigabit platform may provide a more appropriate balance of features and resources.
The Protectli Vault FW4B is the most flexible overall choice for technically capable users because it combines quiet, compact hardware with compatibility across major open-source firewall platforms. The SonicWall TZ280 takes the premium performance position with up to 2.5 Gbps firewall inspection, extensive next-generation security capabilities, and ten network interfaces. For a budget-oriented, streamlined setup, the Ubiquiti Unifi Security Appliance provides VLANs, QoS, VPN, and attractive integration for existing UniFi networks.
The right alternative depends on priorities. Netgate 1100 buyers get a preloaded pfSense+ environment with included updates and support, while the FortiGate range serves organizations that want a defined security-management ecosystem. Fortinet buyers should choose the 40F or 60F according to port and throughput needs, and the security bundle is worth considering when one year of included protection reduces deployment uncertainty. Palo Alto and SonicWall buyers should evaluate licensing and service costs before making a final selection.
Whichever unit you choose, verify the current listing, interface layout, supported functions, management requirements, and subscription terms before ordering. Prices and promotions can change, and the availability of security services may vary by package. A current listing check ensures that the hardware still matches the network, that no required accessories are missing, and that the long-term protection model remains appropriate.